
Foreign Enterprise IPSec Acceleration
No architecture changes, no data inspection—just faster IPSec between Suzhou and Germany headquarters.
A foreign-invested enterprise opened an office in Suzhou connected to its Germany headquarters via IPSec on a FortiGate firewall, under strict mandates for a unified global network architecture and information security compliance. SD-WAN provides a transparent IPSec acceleration channel that passes the encrypted tunnel through intact, making cross-border access noticeably faster and more stable.
- Sites
- Suzhou Office ↔ Germany HQ
- Existing Appliance
- FortiGate Firewall
- Interconnection
- IPSec Site-to-Site Tunnel
- Enterprise Mandate
- Unified global network architecture and information security compliance
The encrypted tunnel passes through intact—SD-WAN simply delivers it faster
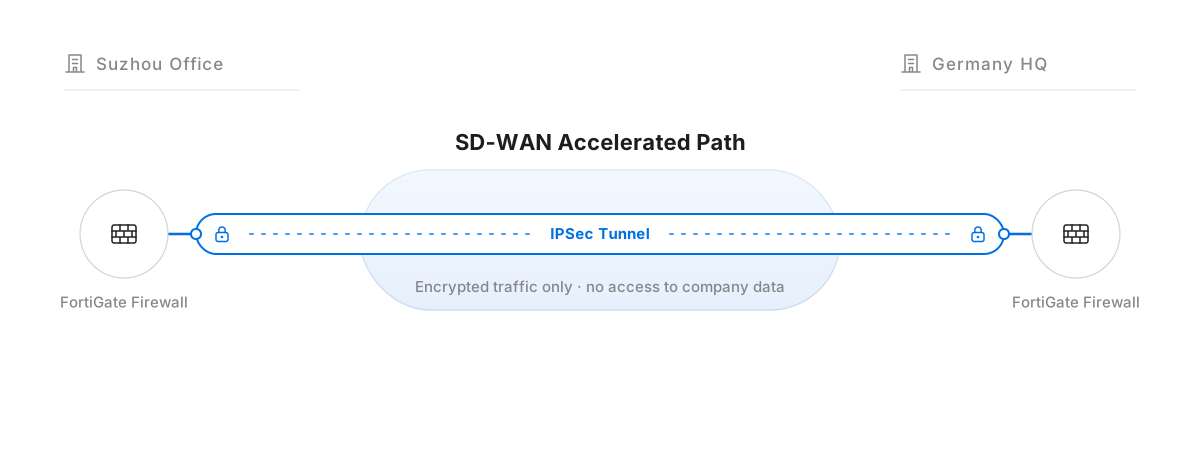
Three Constants
Architecture Unchanged
The Suzhou office and Germany headquarters keep their existing FortiGate-to-FortiGate IPSec tunnel, with configurations, routing, and security policies untouched at both ends.
Data Untouched
SD-WAN carries only already-encrypted IPSec traffic. It neither inspects nor decrypts enterprise data inside the tunnel—it simply delivers the tunnel faster and more reliably.
Policies Intact
The globally unified architecture and information security standards mandated by headquarters remain intact in full, giving the Suzhou office cross-border acceleration within the compliance framework.
The same IPSec tunnel, before and after SD-WAN
Cross-border link quality when accessing Germany headquarters systems from the Suzhou office.
IPSec over Public Internet
Cross-border latencyHighJitter & packet lossHighTunnel stabilityProne to dropsTunnels drop intermittently during peak hours, making HQ systems sluggish to access.
IPSec Accelerated by SD-WAN
Cross-border latencySubstantially lowerJitter & packet lossSignificantly reducedTunnel stabilityConsistently stableEndpoint configurations remain unchanged while access feels near-local.
Have similar multi-region networking needs?
Tell us your site locations, existing links, and the applications you need to access, and we will draw on similar deployments to work out a connectivity approach that fits your business.