
Keep Using Existing Equipment
Retain your existing firewall appliances and IPsec tunnels without building a separate network architecture just for operations in China.
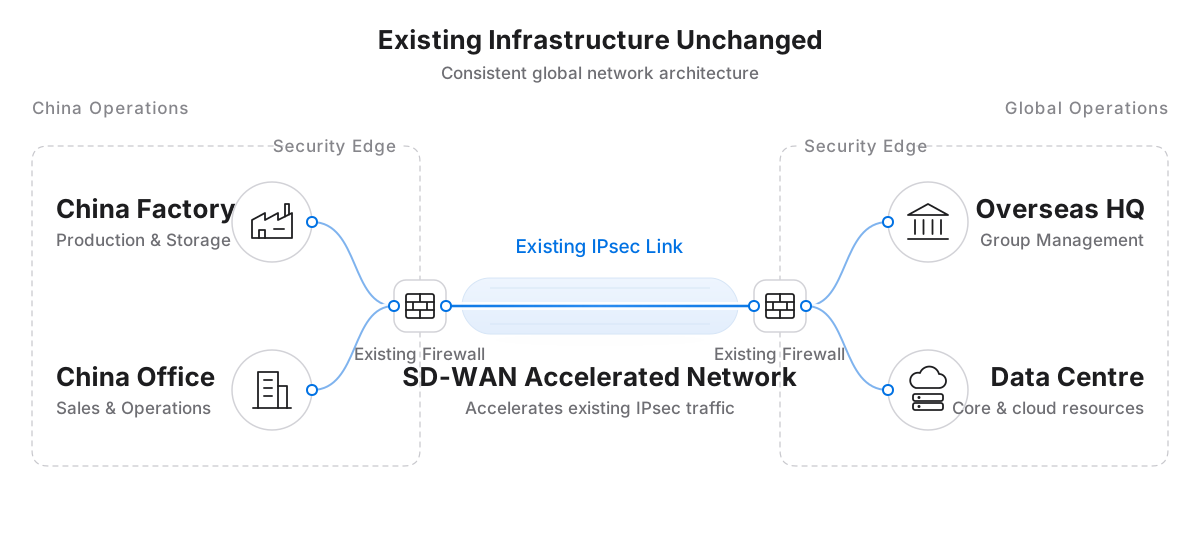
Continue using your existing network infrastructure and firewalls so sites in China follow the network management practices your enterprise already knows.
Retain your existing firewall appliances and IPsec tunnels without building a separate network architecture just for operations in China.
Keep your global network architecture and security posture consistent, extending headquarters access and operations rules without the overhead of managing two parallel systems.
Carry existing IPsec traffic between China and global sites over an accelerated SD-WAN network.
IPsec tunnels are still established between your existing firewalls at both ends while SD-WAN accelerates transit in between, preserving your established connectivity relationships.
Improve cross-region connectivity for production systems, engineering files, and daily collaboration. Specific access methods and paths are planned in accordance with local regulations, carrier conditions, and enterprise security policies.
Assess the current network first and plan onboarding around it so China and overseas IT teams can work with a shared technical model.
Existing firewalls such as FortiGate and Palo Alto can integrate through their current IPsec setups, with clear operational responsibilities across devices, routing, and policies.
Enterprises running Cisco SD-WAN can evaluate integration options around their current sites and orchestration framework to keep global architecture and management rules aligned.
Share your locations in China, overseas headquarters, existing firewalls, and connectivity setup so we can plan accelerated access and coordination between your local and global teams.